Operational Vendor Risk Context You Can Act On
The ground-breaking platform that combines internal and external third-party AI risk analysis, to speed up vendor assessments, secure AI adoption, and act on real-time threats.
The Paradigm Shift Required In the AI Era
The integration of third-party AI and autonomous agents into the enterprise ecosystem has fundamentally broken traditional security and procurement models. To secure an organization today, security teams must undergo a massive paradigm shift in how they view, assess, and manage third-party risk.
Introducing Shift's Context-Driven Vendor Security Platform
Shift is the only platform that unifies external risk assessments, internal activity monitoring, business context, and internal policies, delivering the complete operational context required to enforce the right controls and effectively respond to threats:
External Vendor Risk Assessment
Vendor provided data, Trust Centers, Threat Intelligence
Internal Vendor Footprint
Who and What is active inside the network? Has access changed?
Business Context
Digital asset criticality, ownership, users, and regulatory scopeHR roles, departs and leave
Your Policies
Should a vendor have access to your resource? What data types can the vendor access?
Full Vendor Discovery
Uncovers every vendor in your environment, from officially procured to unauthorized Shadow IT and hidden Shadow AI tools, to eliminate blind spots.
Back to platform
Third-Party AI Exposure
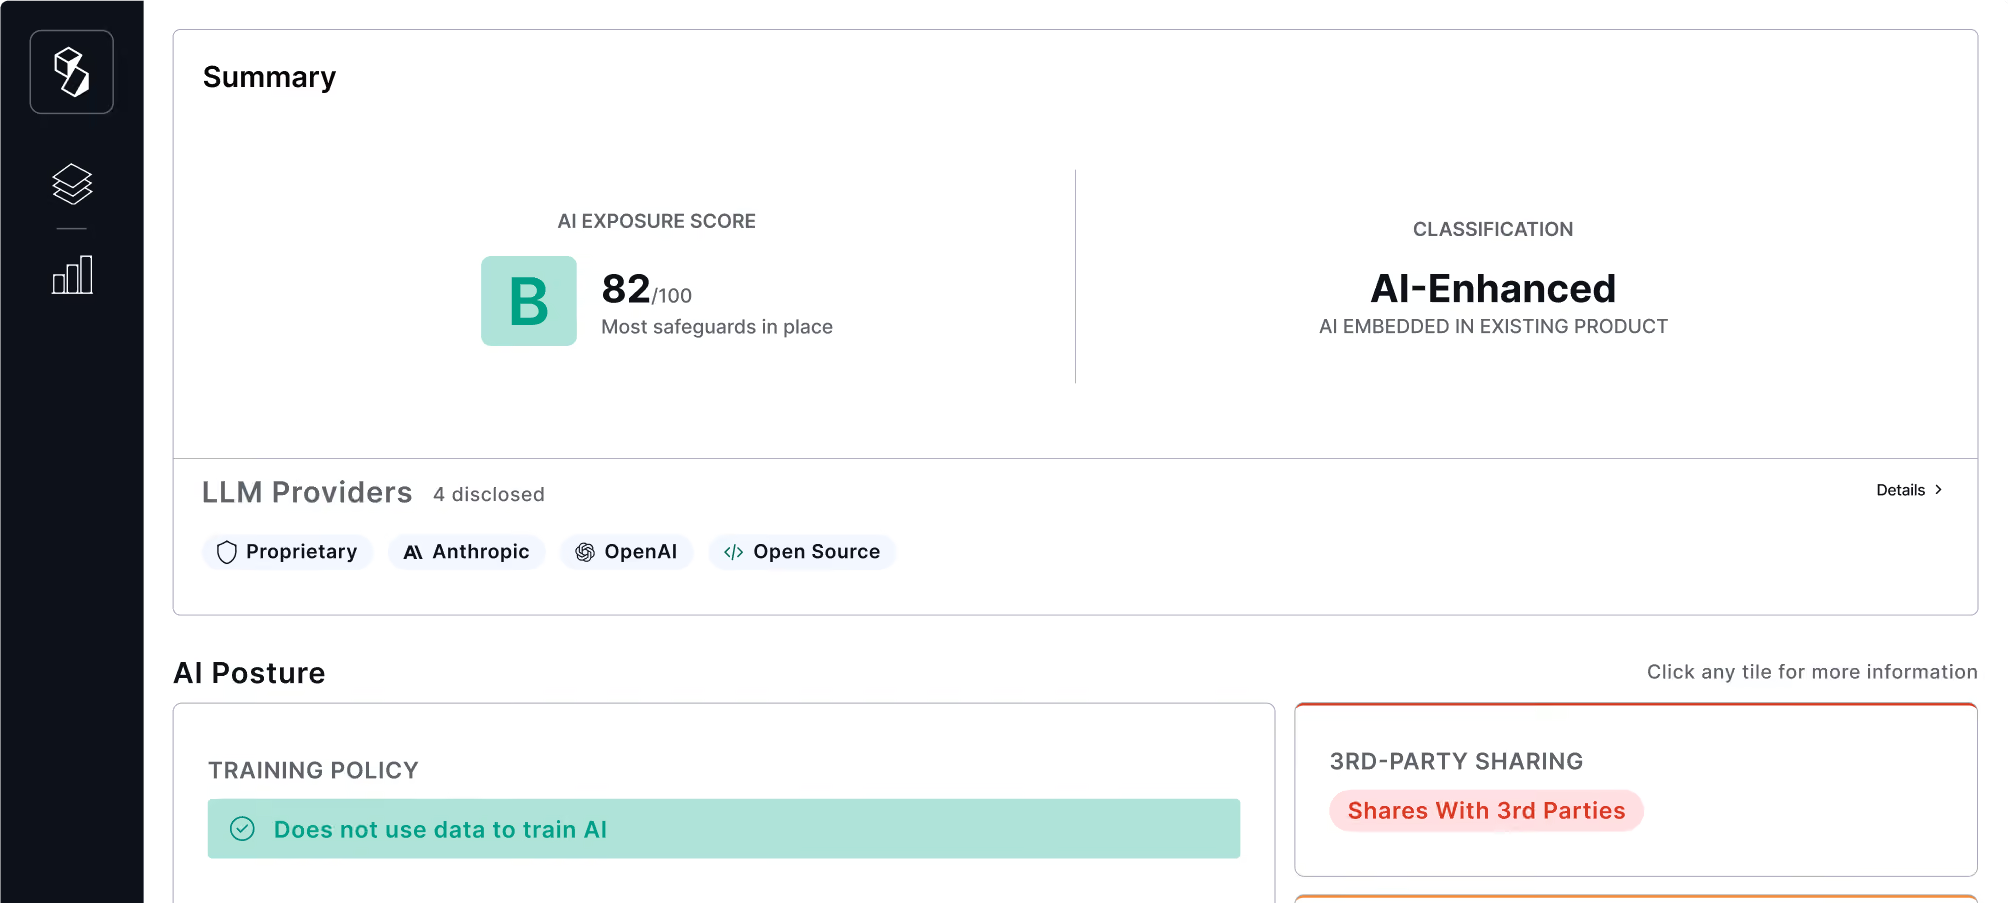
Uncovers hidden AI, preventing data leakage, and strictly restricting agentic access to prevent exposure of critical internal systems and data.
Back to platform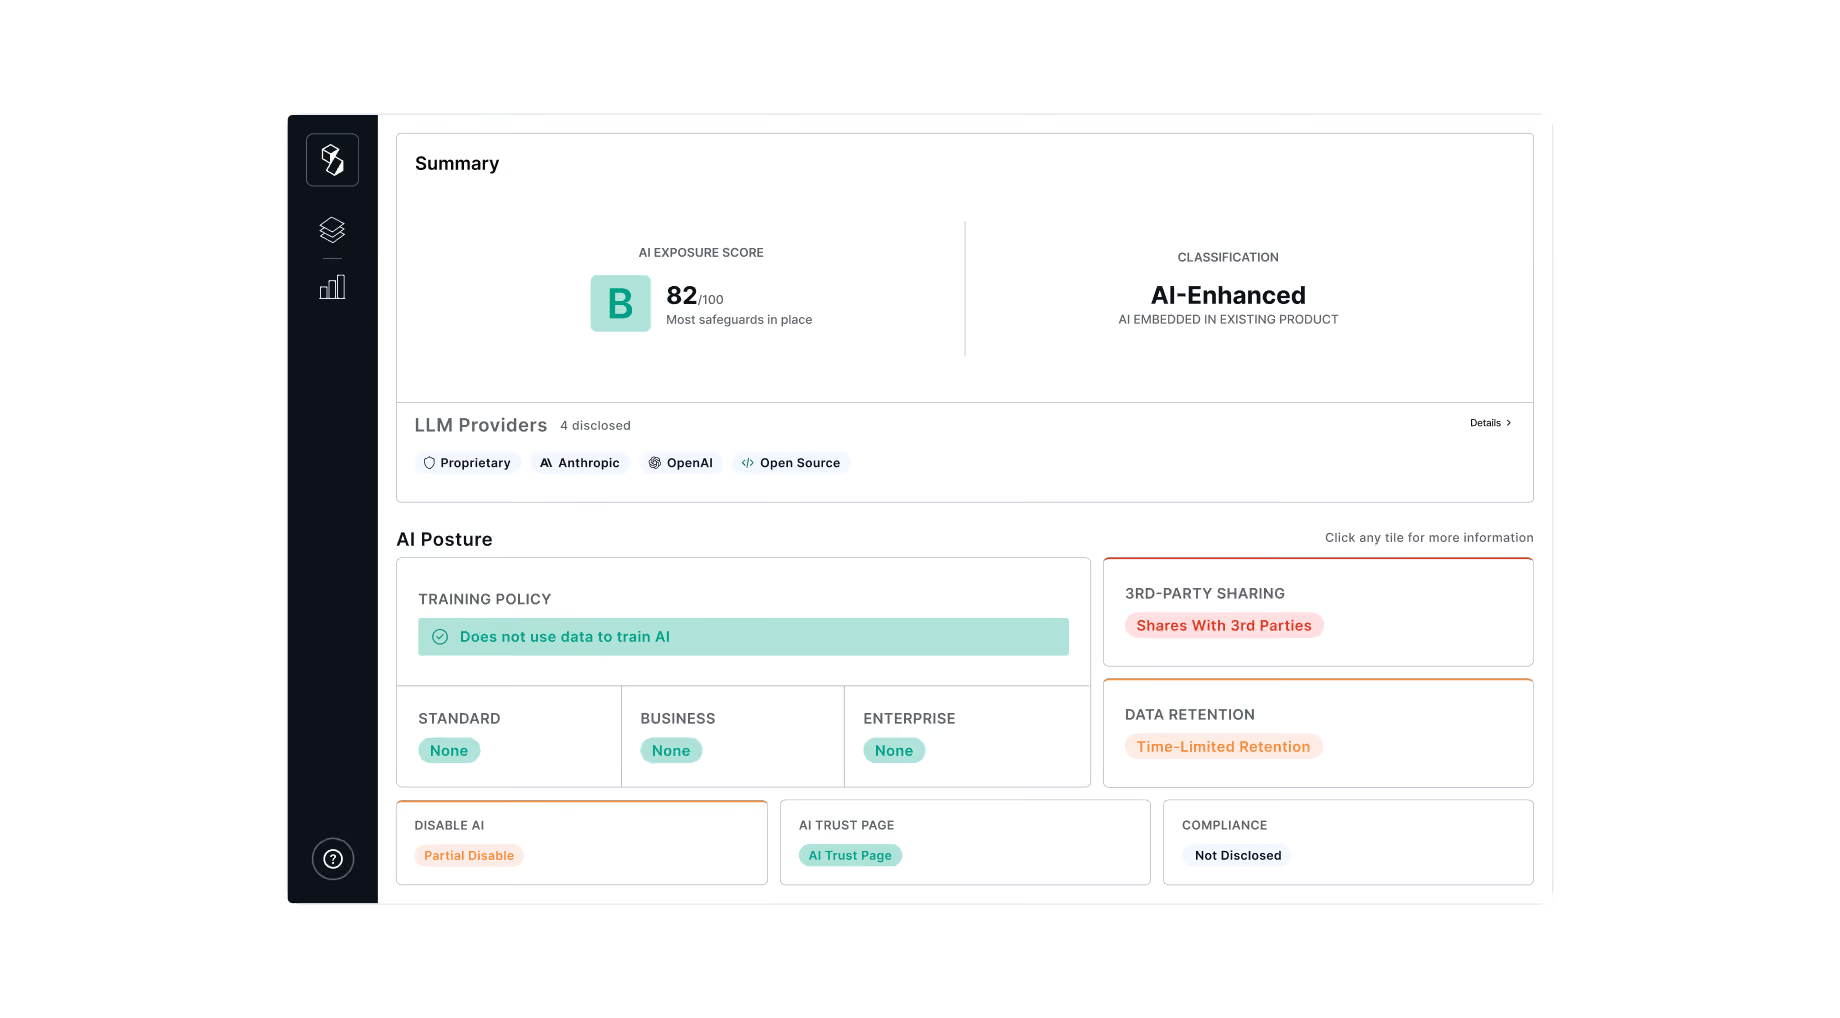
Agentic Vendor Assessments
Automatic gathering of evidence-backed data, eliminating manual work and providing real-time, provable vendor risk visibility with zero friction.
Back to platform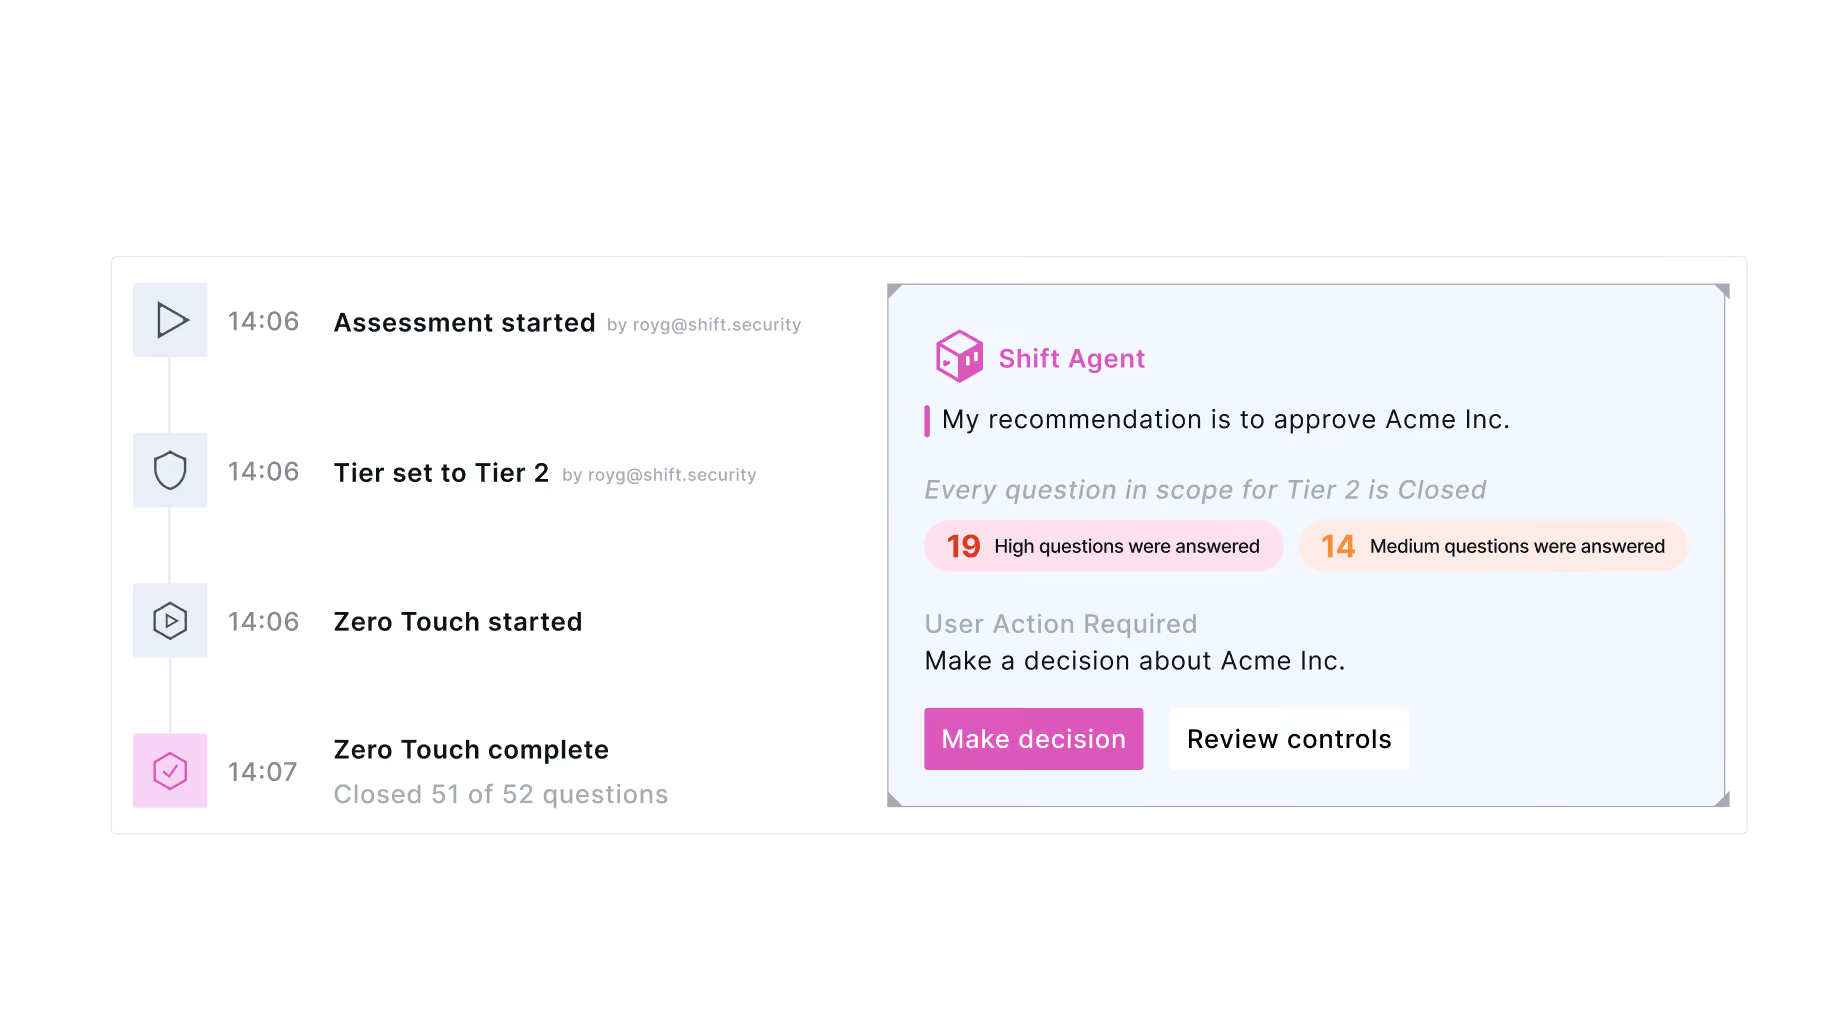
Attack Surface Reduction
Proactively shrink your attack surface by ensuring only authorized, secure vendors operate within your environment.
Back to platform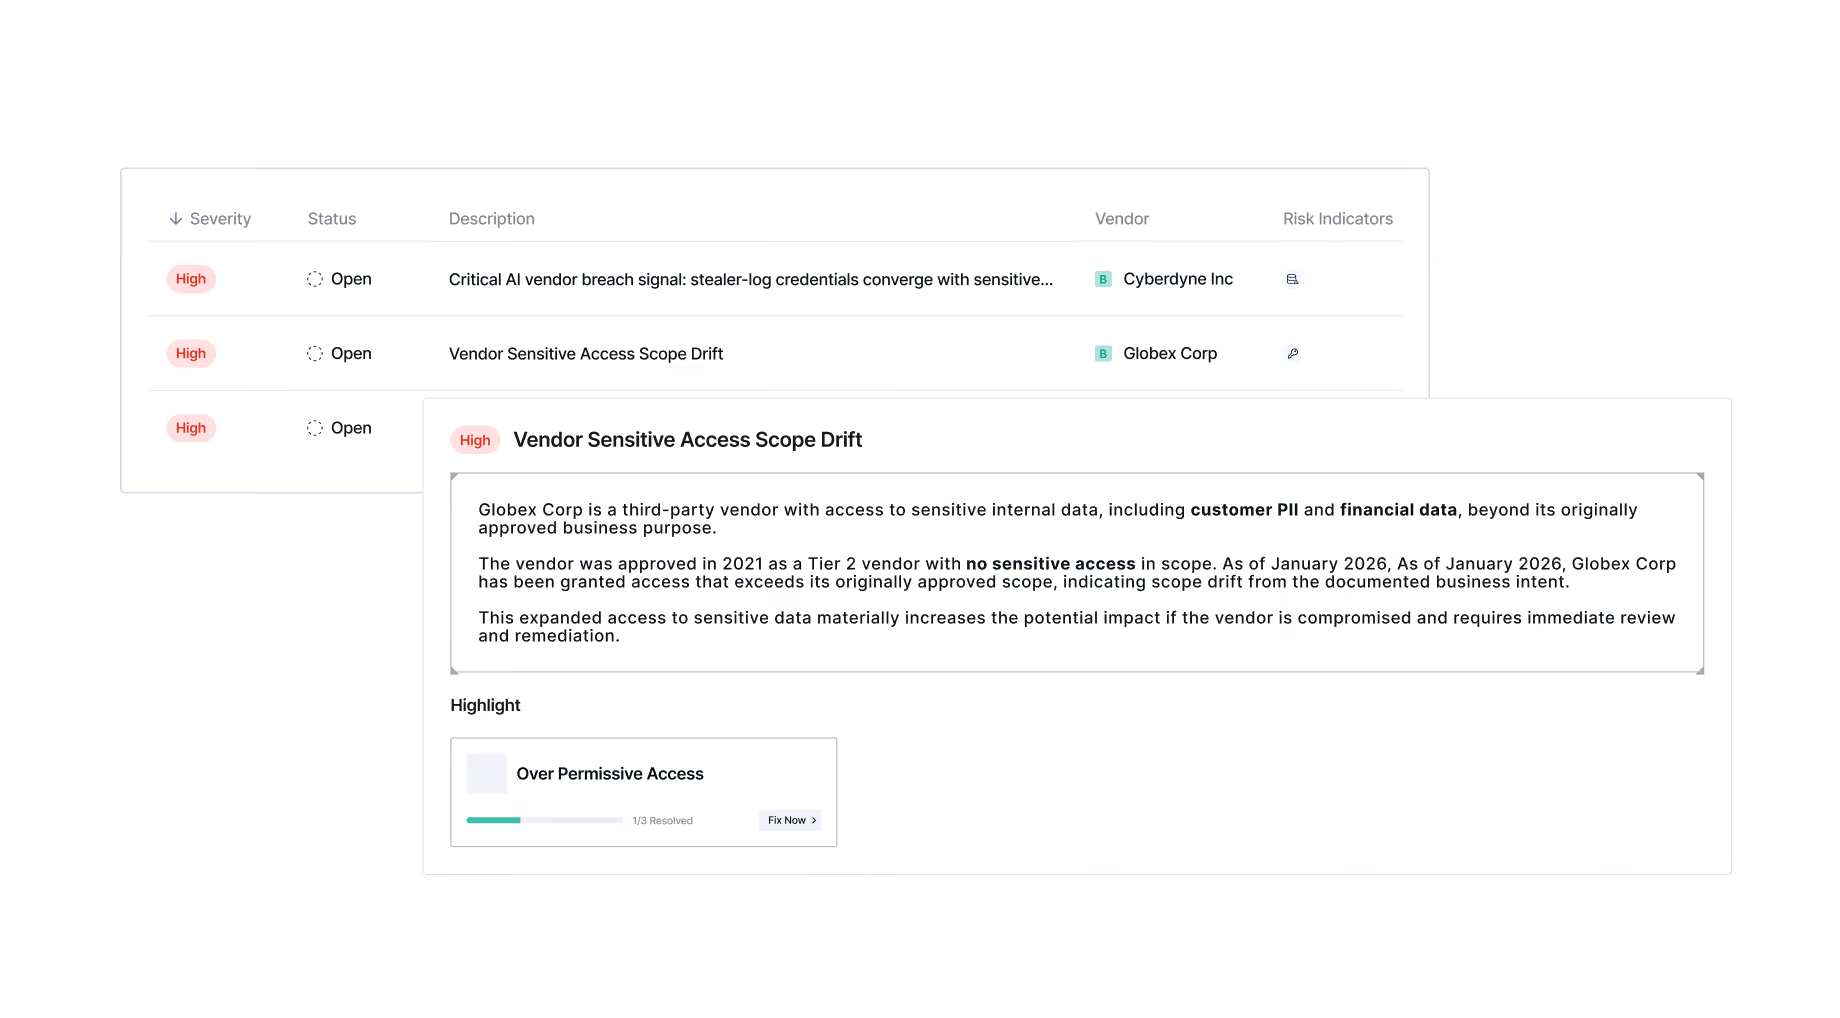
Vendor Threat Detection and Response
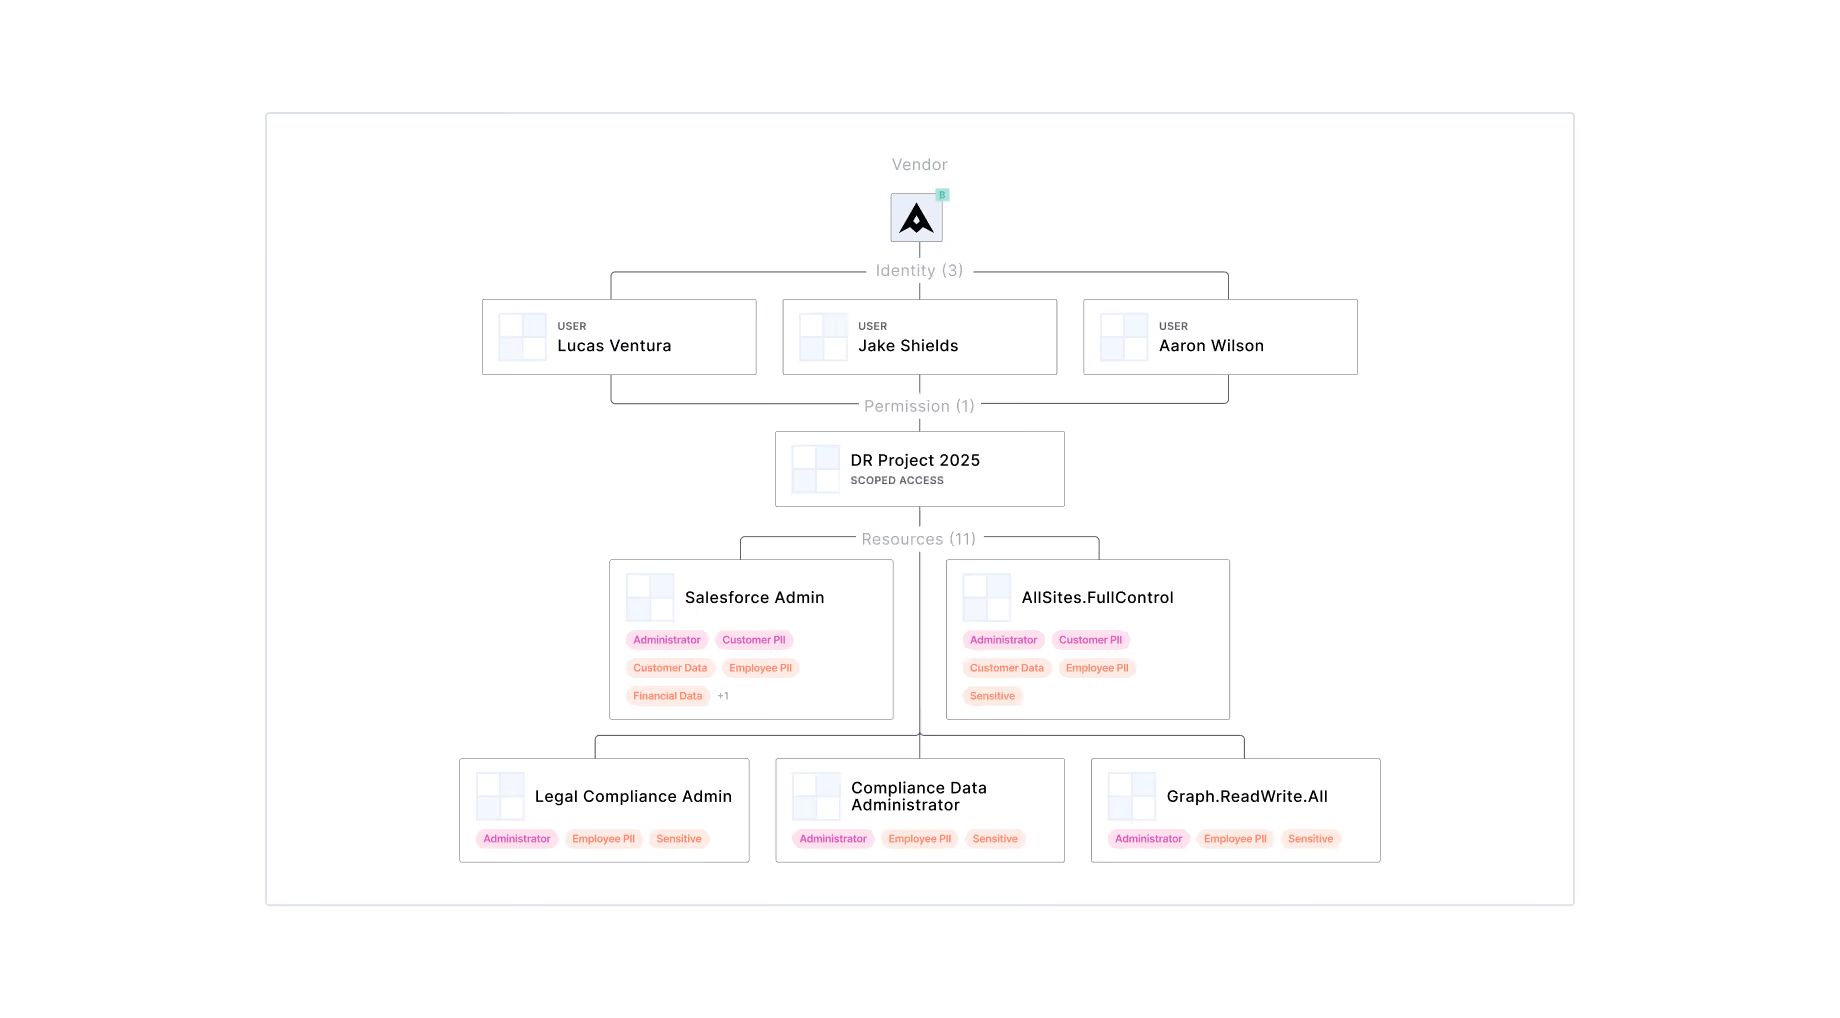
Monitors threat signals and analyzes your potential blast radius, enabling effective threat response and containment of supply chain attacks.
Back to platform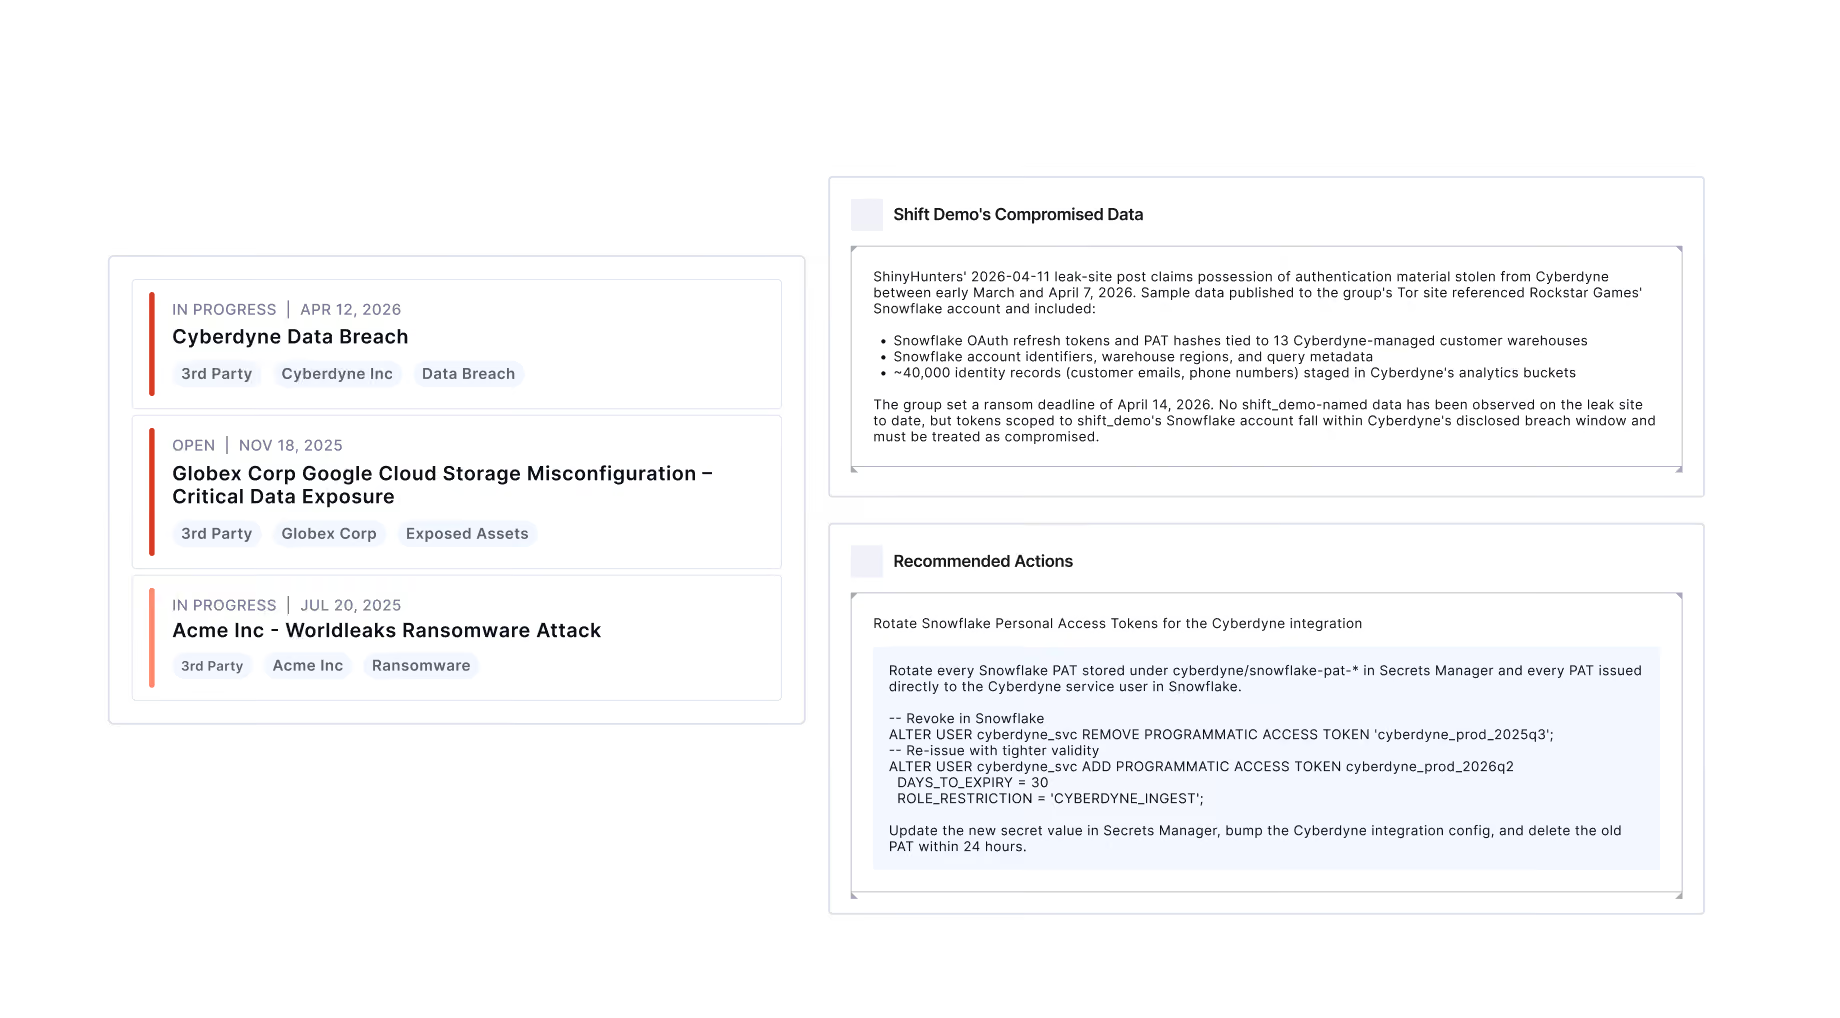
Context That Enables Actionable Security
Looking beyond publicly available data, Shift dives deep into your environment, delivering full context on vendors’ internal footprints, integrations with your business systems, and your specific policies. This comprehensive context makes the difference that enables it to empower Security Operations to actively minimize exposure, detect hidden anomalies, and stop supply chain attacks before a breach occurs
External Vendor Risk Assessment
Vendor provided data, Trust Centers, Threat Intelligence
Internal Vendor Footprint
Who and What is active inside the network? Has access changed?
Business Context
Digital asset criticality, ownership, users, and regulatory scope, HR roles, departs and leave
Your Policies
Should a vendor have access to your resource? What data types can the vendor access?
Improving Enterprise Resilience By Enhancing GRC and SecOps Collaboration
When GRC and SecOps operate in silos, the enterprise is fragile. SecOps drowns in alerts without critical context, while GRC writes theoretical policies that can't be enforced. By bringing them together, Shift creates a continuous feedback loop that improves organizational resilience: the ability to withstand, respond to, and recover from disruptions.
GRC
SecOps
Key Use Cases
Vendor Onboarding and Offboarding
Shift streamlines vendor onboarding by providing a detailed risk assessment and immediately applying policy-based access restrictions. During offboarding, it guarantees complete termination, verifying all vendor access is definitively revoked so absolutely no unauthorized entry points remain.
Safe Third-Party AI Adoption
Shift ensures safe AI adoption by discovering all AI tools and agents actively operating in your environment. It detects access drifts, alerts on behavior changes, and continuously assesses risks and data access to prevent exposure.
Third-Party Policy Enforcement
Shift Security turns static paper policies into active enforcement. It continuously monitors vendor activities, sends real-time alerts on policy violations, and automatically blocks unauthorized access to prevent breach and exposure.
Attack Surface Reduction
Shift Security reduces your attack surface by mapping third-party AI exposures and interfaces. By continuously discovering shadow AI and IT tools, stale access, and over-permissioned vendors, Shift eliminates unauthorized entry points.
Threat Detection and Response
Shift Security provides third-party Threat Detection and Response by integrating active threat intelligence with internal access context. It analyzes potential blast radius and enables real-time containment actions to prevent breach and exposure.
Supply Chain Attack Containment
Shift Security provides instant Supply Chain Attack Containment by detecting 3rd-party and Nth-party threats, analyzing the blast radius, and mapping potential breach paths. Combining threat intelligence with deep access context, Shift isolates compromised vendors and revokes access to neutralize attacks immediately.
FAQs
No. Shift Security integrates with existing GRC tools like ServiceNow and OneTrust to modernize your program over time.
Shift Security delivers comprehensive AI exposure management by discovering shadow AI tools, mapping all AI assets operating within your environment, and continuously monitoring agentic behavior and data access paths to flag deviations from approved business policies.
Yes, it does. Unlike solutions that only surface risk scores, Shift Security provides active access policy enforcement, enabling security teams to set guardrails, issue alerts, and block or isolate unauthorized or over-permissioned third-party access in real time.
When a vendor vulnerability or breach is disclosed, Shift Security performs dynamic blast radius mapping and custom impact analysis. It identifies exactly which corporate data, systems, and identities are exposed, enabling rapid containment and targeted incident response.
Shift supports continuous oversight and enables enforcement of access controls required by mandates like DORA, SEC, and NYDFS.